Single-Tenant Security: Strengthening HIPAA-Aligned Controls for ABA Practices
The HIPAA Security Rule asks an ABA practice to show three kinds of safeguards: administrative, physical and technical, backed by written policies and business associate agreements. A single-tenant EHR does not satisfy those duties for you. A dedicated database and practice-specific encryption keys make several of them easier to demonstrate, scope and document.
Families trust an ABA practice with some of the most personal records in healthcare, and most of those records belong to children. Client files hold diagnostic assessments, FBAs, BIPs, session-by-session behavior data and incident reports. RBTs collect much of that data on tablets in clinics, homes and schools. Every one of those places falls inside what the Security Rule asks you to protect.
What does the HIPAA Security Rule require an ABA practice to show?
The rule requires a practice to protect the confidentiality, integrity and availability of all electronic protected health information (ePHI) it creates, receives, maintains or transmits. Those general duties are set out in 45 CFR 164.306. The same section lets a practice choose measures that fit its size, complexity, technical setup and costs. Some implementation specifications are required. Others are "addressable," which means you assess each one, then implement it or document why an alternative is reasonable.
An inquiry from the HHS Office for Civil Rights, a breach investigation or your own periodic review will look for evidence in five areas:
- Administrative safeguards under 45 CFR 164.308: a risk analysis, risk management, a named security official, workforce access procedures, training, incident procedures and a contingency plan.
- Physical safeguards: facility access, workstation use and security, and device and media controls.
- Technical safeguards under 45 CFR 164.312: unique user IDs, emergency access, automatic logoff, encryption, audit controls, integrity, authentication and transmission security.
- Business associate contracts with every vendor that handles ePHI for you, including your EHR.
- Documentation of policies, procedures and assessments, kept for six years under 45 CFR 164.316.
NIST's guide to implementing the HIPAA Security Rule maps each standard to practical activities for regulated entities of every size. Smaller practices can also work through the Security Risk Assessment Tool from ONC and the HHS Office for Civil Rights. ONC says the tool's target audience is small and medium providers.
Where does an EHR's architecture make those safeguards easier?
Architecture matters most where a safeguard depends on knowing exactly where ePHI lives and who can reach it. In a multi-tenant EHR, many practices share one application and one database, and software rules keep their rows apart. In a single-tenant EHR, each practice runs on its own application, database and encryption keys. Lumenality uses the single-tenant model for every customer practice.
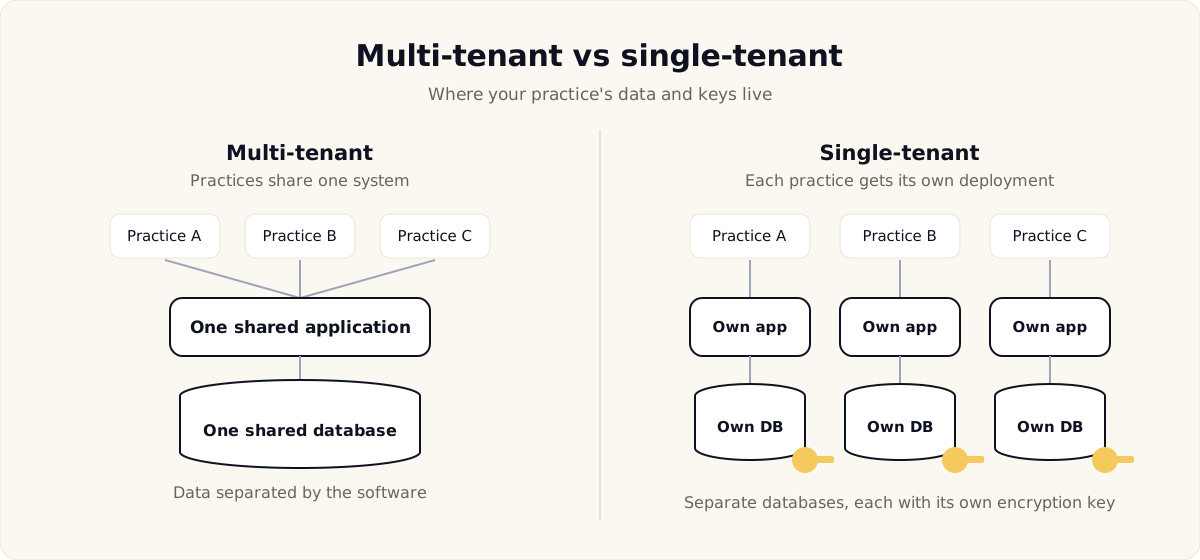
Single tenancy supports specific Security Rule tasks:
- Risk analysis scope. Your inventory of systems that hold ePHI can name one dedicated database, not a share of a pooled one.
- Information system activity review. The rule asks you to review audit logs and access reports regularly. A log from a dedicated deployment records only your own staff, which makes that review easier.
- Access control. Roles and permissions are set for your BCBAs, RBTs and billers without touching another organization's settings.
- Contingency planning. Your plan must cover data backup and disaster recovery, so ask the vendor how it backs up and restores one practice's database.
- Incident containment. A problem in another customer's deployment is far less likely to reach a database it never shared with you.
For a fuller side-by-side of the two models, including where multi-tenant is a reasonable choice, see our single-tenant vs. multi-tenant comparison.
Why do practice-specific encryption keys matter?
Practice-specific keys put the encryption boundary in the same place as the database boundary. Encryption at rest and in transit are addressable specifications under 45 CFR 164.312, so you must assess them and record your decision. Lumenality encrypts stored data with AES-256 and protects data in transit with TLS 1.2 or higher. Each practice's deployment has its own encryption keys.
Encryption is only as strong as the protection around its keys. If every customer's data sat under one shared key, a single key exposure would affect every customer at once. Separate keys limit that exposure to one practice. NIST's recommendation for key management covers how keys should be protected across their whole lifecycle. When you document your encryption decision, record which keys protect your data and who manages them.
Which safeguards stay with your practice?
Most of them do, whichever EHR you choose. HIPAA compliance is shared between a covered entity and its business associates. Lumenality signs a Business Associate Agreement with every customer and is hosted on SOC 2-compliant providers. Inside each deployment it provides role-based access control down to the field level, MFA, configurable session timeouts and an audit trail of who opened each record.
Your practice still owns the work no vendor can do for you:
- Run and update the risk analysis, and act on what it finds.
- Name a security official and write the policies the rule requires.
- Train staff, including RBTs who carry tablets into homes and schools.
- Grant access by role, and remove it the day someone leaves.
- Review the access log on a set schedule and look into anything unusual.
- Secure workstations and tablets, which fall under the physical safeguards.
- Keep your documentation for six years and update it when things change.
An EHR that isolates your data and logs every record view makes that work easier to evidence. To test any vendor's answers before you sign, use our security checklist for EHR vendors. Complete data exports matter too if you ever change systems, and our post on avoiding vendor lock-in explains what to ask for.
Putting it together
A single-tenant deployment will not write your policies or train your staff. What it gives your safeguards is a clear boundary: one practice, one database, one set of keys and one access log. To see how those controls sit alongside scheduling, session data, authorizations and billing, explore Lumenality for ABA or request a demo. *One place, where health happens.*
*This article was created with AI assistance and reviewed by the Lumenality team.*