Deep Dive: Single-Tenant EHR Security for ABA Practices
Before you sign with any EHR vendor, get specific answers to eight questions. Ask where your data lives and who holds the encryption keys. Ask how access is limited by role and whether every record view is logged. Then ask about the BAA, incident reporting, backups and how you get your data out.
Why should an ABA practice question its EHR vendor about security?
A vague answer from a vendor becomes a risk your practice inherits. ABA client files hold developmental histories, FBAs, BIPs, session-by-session behavior data and incident reports, and most clients are children. RBTs record data on tablets in clinics, homes and schools, so the record is touched in many places by many people. Your EHR vendor is a business associate under HIPAA, but the duty to protect that information stays with your practice too.
The questions below follow the order an owner would naturally ask them. Each one notes what a strong answer sounds like and how Lumenality answers it. For the regulatory background first, our post on HIPAA-aligned controls for ABA practices walks through the safeguards the Security Rule expects.
Where does our data live, and who shares it with us?
A strong answer names the architecture plainly. In a multi-tenant EHR, many practices share one application and database, and every query must filter rows correctly every time. In a single-tenant EHR, each practice has its own deployment and its own database. Security engineers describe the difference as blast radius: how far a single failure can spread.
Lumenality gives every customer practice its own dedicated deployment and database, not a slot in a shared pool. No shared table holds your records next to another organization's, so no cross-tenant query can mix them. No architecture removes every risk, but isolation narrows the paths an incident can travel. Our single-tenant vs. multi-tenant comparison covers the trade-offs, including cost.
Who holds the encryption keys?
The answer you want is that your data sits under keys used for your practice alone. Also ask which algorithms protect stored data and which protocol versions protect network traffic. NIST's TLS guidelines require government servers and clients to support TLS 1.2 and TLS 1.3, which makes a useful benchmark. A vendor should answer both questions without hesitation.
Lumenality encrypts data at rest with AES-256 and in transit with TLS 1.2 or higher. Each practice's deployment has its own encryption keys, so the key boundary matches the database boundary.
How is access limited by role?
Access should follow the job, down to individual fields where needed. An RBT, a BCBA and a billing specialist each need different parts of the same client record. HIPAA's technical safeguards include unique user IDs, person authentication and automatic logoff after inactivity. Ask how roles are defined, who can change them and how quickly access ends when someone leaves.
Lumenality applies role-based access control at the field level and supports MFA and configurable session timeouts. Timeouts matter when tablets move between staff or sit in a client's home.
Is every record view logged, and can we read the log?
A good vendor logs every view of a client record, not only edits, and lets your admin read that log. The same technical safeguards include audit controls that record and examine activity in systems holding ePHI. Your practice must also review that activity regularly, so the log has to be readable on your side. Ask how far back the log goes and whether you can export it.
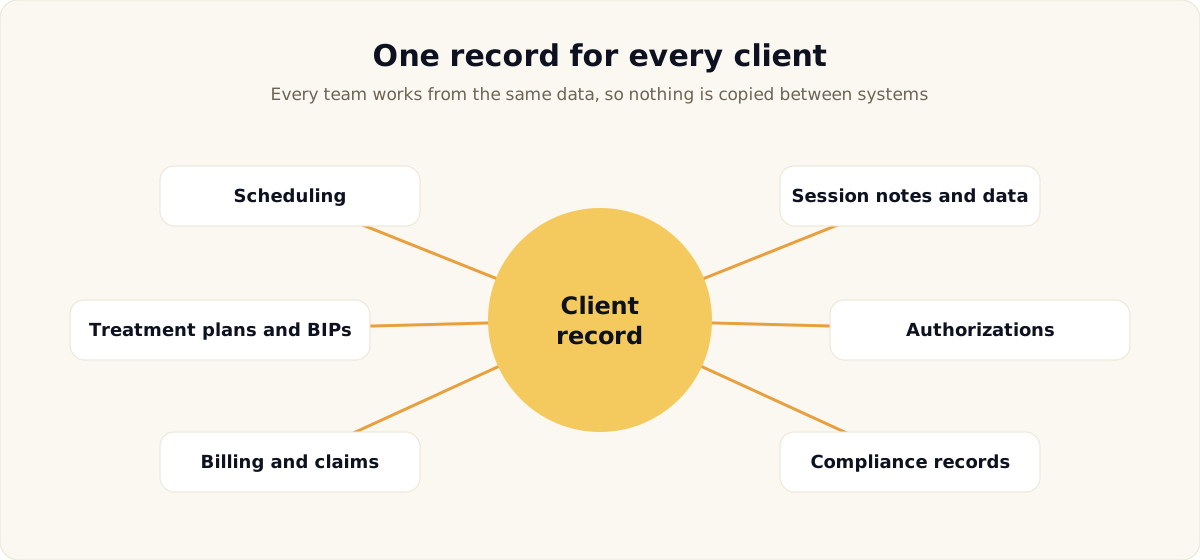
Lumenality keeps an audit trail of who opened each record. Scheduling, session data, treatment plans, authorizations and billing all share one client record. That leaves one set of access rules to configure and one trail to review.
What does the BAA commit the vendor to?
The BAA should commit the vendor to the Security Rule and to reporting security incidents to you. Those terms are not optional. Under 45 CFR 164.314, a business associate contract must include them and must flow them down to subcontractors. Ask who the vendor's subcontractors are, including hosting.
Lumenality signs a BAA with every customer and is hosted on SOC 2-compliant providers. When any vendor mentions SOC 2, ask whether the report covers its own application or only its hosting provider. The two scopes are different.
How will we hear about an incident?
You should hear promptly, from a named contact, through a channel agreed in writing. Ask the vendor to describe its incident process in plain steps: detection, containment, notice to you and follow-up. Ask how an incident in one customer's environment is kept from reaching others. In a single-tenant design, the answer starts with separate deployments and databases.
How are backups handled?
A vendor should describe how it backs up your data and how it would restore it. Your own contingency plan must cover data backup and disaster recovery, so you need those answers in writing. Ask how often backups run, where they are stored and whether they are encrypted. Ask how long a restore of your practice's data would take.
How do we get our data out?
You should be able to export everything, in a usable format, whenever you ask. Ask what an export contains, what it costs and what notice is required to leave. Lumenality provides full CSV exports of clinical, billing and operational data on request at any time. When a practice leaves, it gets the same exports with 30 days' notice and no exit fees. Our post on avoiding vendor lock-in explains what a complete export should include.
Which frameworks should a vendor's answers line up with?
A vendor's answers should map to a recognized framework, even if the vendor never names one. The NIST Cybersecurity Framework organizes security work from governance through recovery. The HHS 405(d) program publishes Health Industry Cybersecurity Practices for healthcare organizations. Good answers cover identifying risks, protecting data, detecting problems, responding and recovering.
Putting the checklist to work
Bring these eight questions to every demo, and ask for the answers in writing. Compare how specific each vendor is, not how confident it sounds. Our guide to choosing an EHR for a small ABA practice covers the clinical and billing questions to ask alongside these. To see how Lumenality answers them in a live walk-through, explore Lumenality for ABA or request a demo.
*This article was created with AI assistance and reviewed by the Lumenality team.*